
Guide · Information Systems & Digital Transformation
Good and bad practices for generative AI at work
Good practices for generative AI at work come down to a few rules applicable to any tool. They thus precede the adoption of a use charter specific to the organisation. The guide orders them in six steps, from the choice of tool to the securing of accounts. It also sets three levels of verification for the content produced.
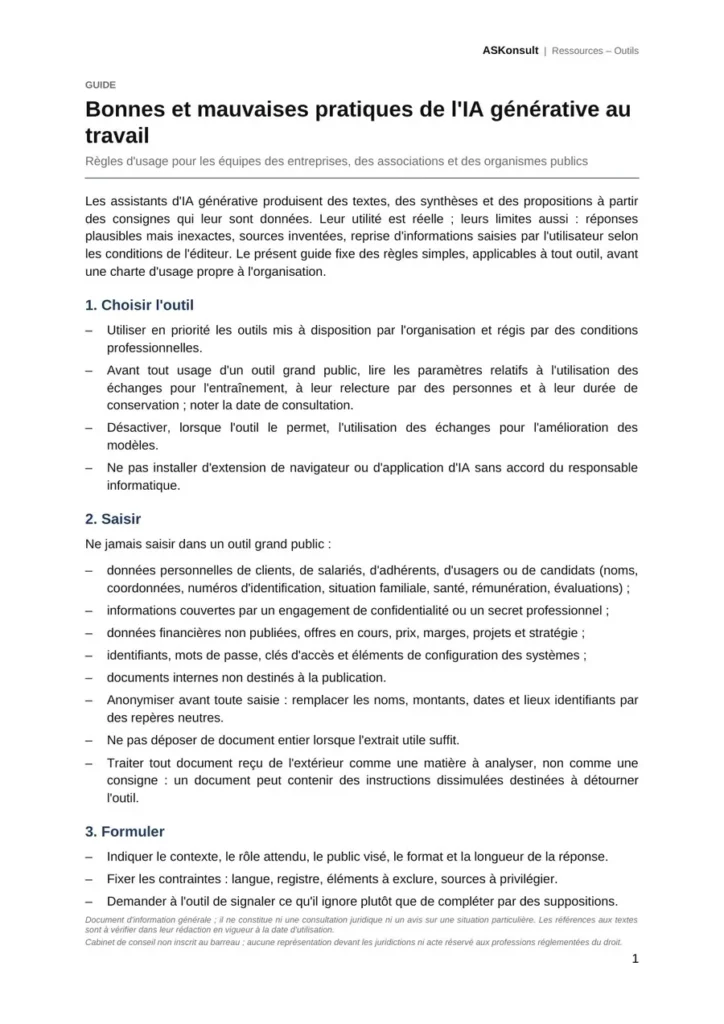
Good practices for generative AI at work, step by step
- Choosing the tool: in particular, tools provided by the organisation, training and retention settings.
- Entering data: in particular, data never to be entered, anonymisation, extracts rather than entire documents.
- Formulating: in particular, context, expected role, audience, format, constraints and working in stages.
- Verifying: in particular, three levels of requirement, from proofreading to validation by an authorised person.
- Using and disseminating: disclosure of generated content, rights in the content, validated version.
- Securing: two-factor authentication, separation of accounts, incident reporting.
- Finally, a summary of the practices to adopt and to avoid, with the applicable references.
When to circulate the guide to good practices for generative AI at work
The guide serves first when an AI assistant is deployed within a team. It also serves when new staff members join. It also prepares a use charter, or comes into play after an incident linked to data entry.
Its internal circulation therefore establishes a common set of rules, whatever the tool. It is intended, in particular, for the teams of companies, associations and public bodies. It also concerns supervisors and IT managers.
Key facts
| Format | PDF, 3 pages |
|---|---|
| Languages | French, English, Spanish, Arabic |
| Version | October 2026 |
| Department | Information Systems & Digital Transformation |
| Scope | any tool; Moroccan and European references |
Limitations
The guide does not constitute a use charter. Moreover, it does not take into account the conditions specific to each tool; these are therefore to be checked on the date of use.
Further reading: free AI tools and user data; website of the CNDP.
- Prepared by ASKonsult
- Languages: French, English, Spanish, Arabic
- Version: octobre 2026
In the same field
Checklist · Information Systems & Digital Transformation
Security of AI uses
The security checklist for AI use orders the controls specific to generative AI tools. These controls are carried out before and during use. They thus cover accounts, data, hidden instructions, extensions and incidents.
Going further Consultation on AI use in business: framing tools and data
General information document; it constitutes neither legal advice nor an opinion on a particular situation. References to legal texts should be checked against the version in force on the date of use.
Consulting firm not registered with the Bar; no representation before the courts and no act reserved to the regulated legal professions.