
Checklist · Information Systems & Digital Transformation
Security of AI uses
The security checklist for AI use orders the controls specific to generative AI tools. These controls are carried out before and during use. They thus cover accounts, data, hidden instructions, extensions and incidents. The checklist also complements the organisation’s security policy.
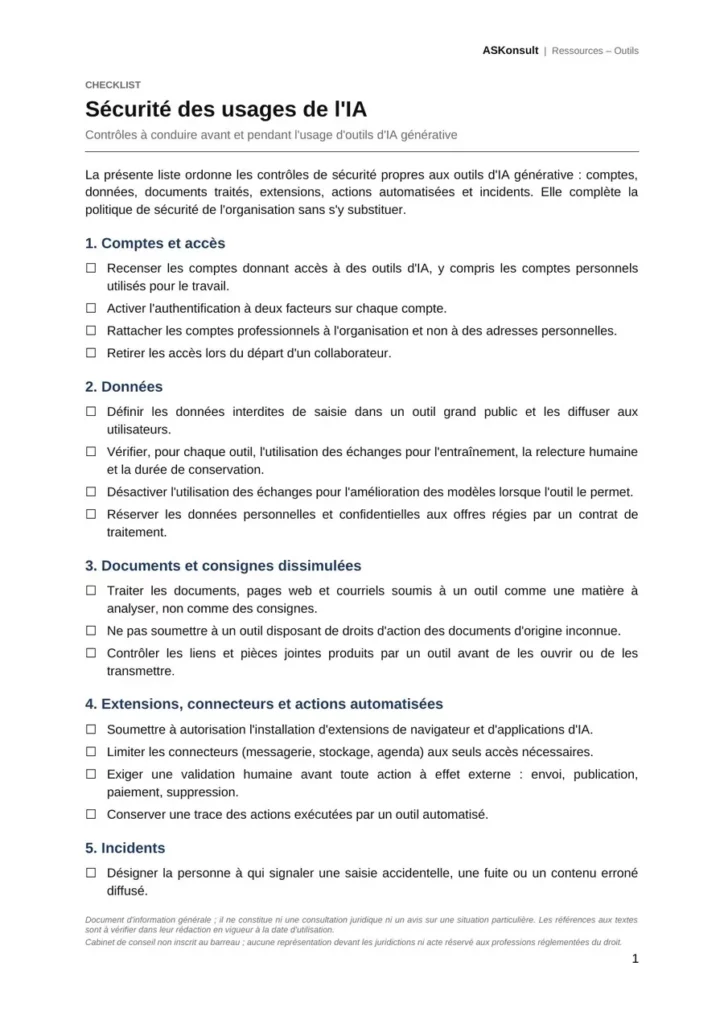
The controls in the security checklist for AI use
- Accounts and access: in particular, inventory, two-factor authentication, removal of access upon departure.
- Data: in particular, data that must not be entered, the conditions of each tool, data processing agreement.
- Documents and hidden instructions: in particular, external content treated as material for analysis.
- Extensions and connectors: in particular, prior authorisation and access limited to what is necessary.
- Automated actions: human validation before any sending, payment or deletion; traceability.
- Incidents: designated person, register, obligations under Laws No. 09-08 and No. 05-20.
- Finally, the Moroccan references and the OWASP sheets on prompt injection.
When to apply the security checklist for AI use
The checklist serves first before an AI tool is opened to teams. Its use is also required when an extension or a connector is installed. In addition, it supports a security audit or the handling of an incident.
Its intended users include, in particular, IT managers and information systems security managers. Data protection officers are also concerned. The checklist thus complements the good practices guide intended for users.
Key facts
| Format | PDF, 2 pages |
|---|---|
| Languages | French, English, Spanish, Arabic |
| Version | October 2026 |
| Department | Information Systems & Digital Transformation |
| Scope | Laws No. 09-08 and No. 05-20 (Morocco); OWASP framework |
Limitations
The checklist is not a substitute for the organisation’s security policy. Likewise, it does not replace a risk analysis specific to each tool.
Further reading: AI and personal data in Morocco; the OWASP sheet on prompt injection.
- Prepared by ASKonsult
- Languages: French, English, Spanish, Arabic
- Version: octobre 2026
In the same field
Guide · Information Systems & Digital Transformation
Good and bad practices for generative AI at work
Good practices for generative AI at work come down to a few rules applicable to any tool. They thus precede the adoption of a use charter specific to the organisation.
Going further Consultation on AI use in business: framing tools and data
General information document; it constitutes neither legal advice nor an opinion on a particular situation. References to legal texts should be checked against the version in force on the date of use.
Consulting firm not registered with the Bar; no representation before the courts and no act reserved to the regulated legal professions.